Text on yellow background: ~70% of real-world attacks happen before a CVE even exists.

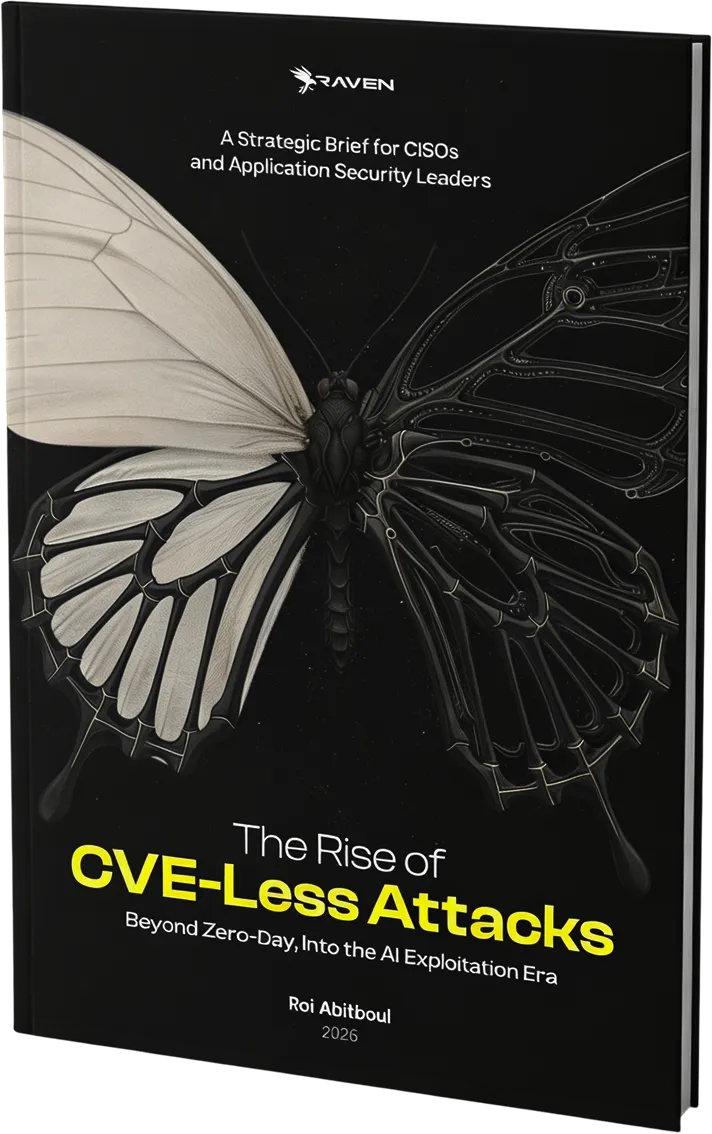
The Rise of 

CVE-Less Attacks

This report examines why enumeration-based security is structurally falling behind — and what it means for how you build protection.
Prevent explotation
Why CVE was never designed to prevent exploitation — and what it actually is
Incident data response
Incident response data showing the scale of pre-CVE exploitation in the wild
AI Tool
How AI tools are widening the gap between exploitation and enumeration timelines
Protection
What it means to move protection upstream, closer to execution

Get Your eBook!

The Rise of CVE-Less Attacks Book Cover

Blog

Raven.io Enters Korea to Stop AI-Driven Attacks
Company News
After an AI-driven campaign hit Korean financial firms, Raven.io enters Korea to stop exploits at runtime, before a CVE exists.
Read more
RASP Is Dying. Runtime Application Security Is Not.
Security
Classic RASP tools are consolidating under the weight of agents, overhead, and language gaps. See how runtime application security is replacing them.
Read more
Scanner Found Zero CVEs? Open Source Supply Chain Attacks | Raven.io
Security
A zero-CVE scan proves your dependencies match no published vulnerability. Open source supply chain attacks are built to pass exactly that test.
Read more