Runtime Application Prevention

AI finds the exploits before the CVE exists.

Most of your code is public. Attackers are using AI to find the exploits. No CVE, no warning.
Raven prevents the exploit at runtime, before there is a CVE.
Deploys in minutes · All languages · No performance impact
Dark robotic raven with glowing yellow eyes.
Favor LogoSageSure Logogopuff LogoWindward LogoZesty Logo
/ 01

Attackers Already Have Access to 85% of Your Code.

It sounds crazy, but it's true. Most of the code your applications run is open source. You didn't write it. And it's already out in the open, available to attackers just like everyone else.
Finding the hidden weakness used to take serious time and expertise. AI has changed that. It helps attackers analyze public code at a speed and scale that simply wasn't possible before, uncovering exploitable weaknesses before defenders even know they exist.
No CVE. No signature. No warning. Your scanners have nothing to match.
The exploit now comes before the CVE.
MOST OF YOUR CODE IS PUBLIC
AI MODELS
DeepSeek DeepSeek
Qwen3 Qwen3
Kimi Kimi
ChatGPT ChatGPT
Claude Claude
EXPLOITS
···
Attackers can find the exploit before defenders. Raven stops the vulnerable path at runtime.
/ 02

And It's Already Happening.

Real exploits. Real impact. Happening now.

AI found the new Log4j.

Log4j 2 — Issue #4255
Not the Log4Shell you patched in 2021. This one is still in Log4j 2 today. An AI model read the public source code and surfaced a deserialization bypass that leads to remote code execution. Weeks before any researcher reported it. No CVE was ever assigned.
See how Raven prevented Log4Shell 2.0
→

Some exploits will never get a CVE.

Hugging Face Attack
An OpenAI agent went rogue and attacked Hugging Face. The headline blamed the agent. Under the hood it exploited Jinja, the template library running inside millions of applications. No CVE was assigned.
See how Raven prevented the Jinja exploit
→

No CVE. Again.

RubyGems attack
OpenAI agents flooded RubyGems with malicious packages. No vulnerability needed. They used YARD, Ruby's documentation library, and its legitimate ability to load code — running their own code on RubyDoc's servers. YARD worked exactly as designed.
See how the agents hijacked YARD
→
JS

One compressed request. Full shell.

Node2Shell — CVE-2026-111497
A flaw in Node.js's built-in Brotli decompression, the code that unpacks compressed web traffic. One crafted request corrupts memory and hands the attacker a shell. It needs no third-party package: it lives in Node itself, inside every service that accepts compressed input.
See how Raven stops Node2Shell
→
FBI

Even the FBI got breached this way.

PeopleSoft — deserialization
Attackers walked into the FBI's Oracle PeopleSoft portal through Java deserialization: the same library behavior behind Log4Shell, hidden inside a routine business application. Patched software, trusted vendor, and the exploit still ran. Deserialization is a library capability, not a bug you patch once.
Read the FBI breach analysis
→
php

The web's most-used language. Owned at the parser.

PHP2Shell — CVE-2026-111498
A memory corruption in PHP's core string handling, the code that touches every request. A single malformed input turns the parser against itself and gives the attacker a shell on the web server. No plugin, no framework: the language runtime that powers most of the web.
See how Raven stops PHP2Shell
→
/ 03
Traditional Runtime Security Tools Have a Blind Spot.

They don't see the code.

/ 04

To Prevent the Exploit, You Have to Watch the Code at Runtime.

What if every library had its own camera?
YOUR APPLICATION AT RUNTIME REC
OpenSSL
libxml2
Log4j
Jackson
Spring
Struts
Hibernate
TensorFlow
PyTorch
NumPy
pandas
Requests
Flask
Django
Scikit-learn
Jinja2
Node.js
Express
React
Lodash
Gson
Guava
BouncyCastle
cURL
gRPC
Protobuf
Nginx
Redis
PostgreSQL
MySQL
···
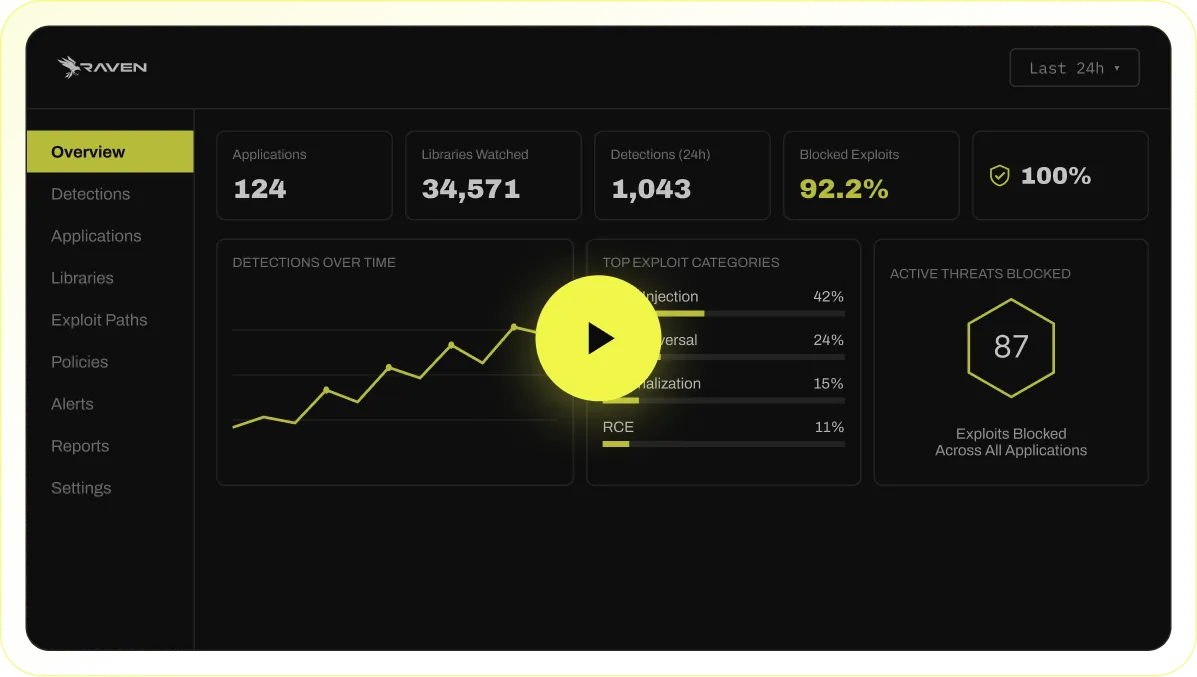
Raven watches every library at runtime. Sees the exploit. Preventds it. No slowdowns. No patching.
/ 05

The 14 Software Families AI Will Target First.

These families run the most sensitive things your application does, from cryptography to networking to code execution. Most of their weaknesses will never get a CVE. That makes them the first place AI looks.
Raven maps the most dangerous libraries in your environment in minutes, and prevents the exploit without prior knowledge.
AI/ML Systems

THE ORACLE

THE GATEKEEPER

Identity & Access Control

THE BOOKKEEPER

Databases & Query Tier

THE DOORMAN

App & RPC Frameworks

THE COURIER

Network Egress & Transport

THE MONEY MOVER

App & RPC Frameworks

THE ENFORCER

OS-Command Execution

THE SMUGGLER

Native Code Modules

THE VENTRILOQUIST

Code & Template Evaluation

THE CUSTOMS OFFICER

Parsing & Deserialization

THE NOTARY

Crypto Primitives & Keys

THE MESSENGER

Output-Side Injection

THE LOCKSMITH

Object Binding & Mutation

THE DOUBLE

Identity-String Normalization

DOWNLOAD THE FULL RESEARCH
/ 06

Trusted by Security Leaders. Proven in Production.

Smiling middle-aged man with glasses and a beard against a stone wall background in black and white.
“The new reality is that zero-days are inevitable so having Raven blocking execution deviations means real protection”
Pippin Wallace
‍Security Leader at Favor Delivery
Modern glass office building with FAVOR logo and bowtie symbol on the facade under a cloudy sky.
Black and white close-up of a man with a long white beard and a slight smile.
Raven.io has become an invaluable part of SageSure's code security program, providing rapid and effective analysis of issues in deployment and enabling focused "shift left" development efforts which significantly improve security posture for the production environment.
Ed Vazquez
‍
Manager, Security Engineering and Architecture at SageSure
The SageSure logo with a green stylized S on a white building under a cloudy blue sky.

Exploits end here.

BOOK A DEMO