


Application-Aware Cloud Threat Hunting
Application-Aware Cloud Threat Hunting
Hunt threats using real application execution - not just infrastructure signals
Book a demo
SOCs hunt threats without application visibility

Infrastructure signals lack application context
Cloud logs, network telemetry, and CSP alerts show where something happened - not what code executed or why.

Alert fatigue without application relevance
SOCs are flooded with detections that can’t be tied to real application behavior, leading to false positives and slow investigations.

AppSec and SOC operate with different truths
AppSec sees vulnerabilities.SOC sees incidents.Neither can answer: Why did the code execute? Is it a feature or an actual attack?
Application-Aware Threat Signals
With Raven, SOC analysts gain deterministic context instead of probabilistic alerts.
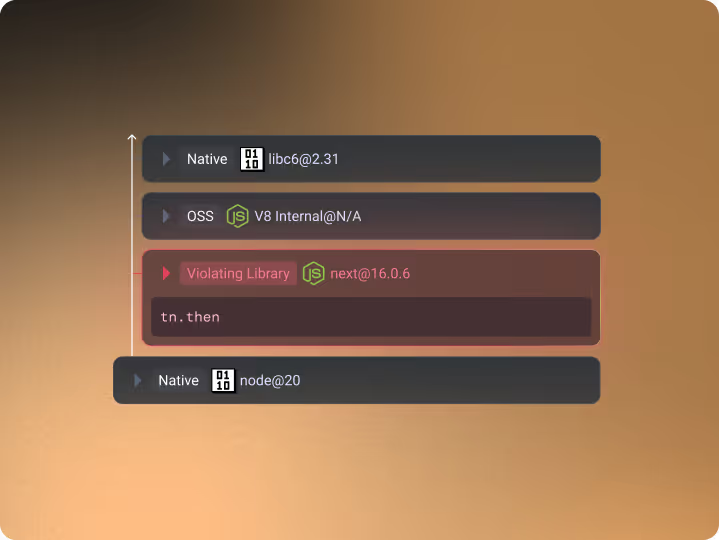
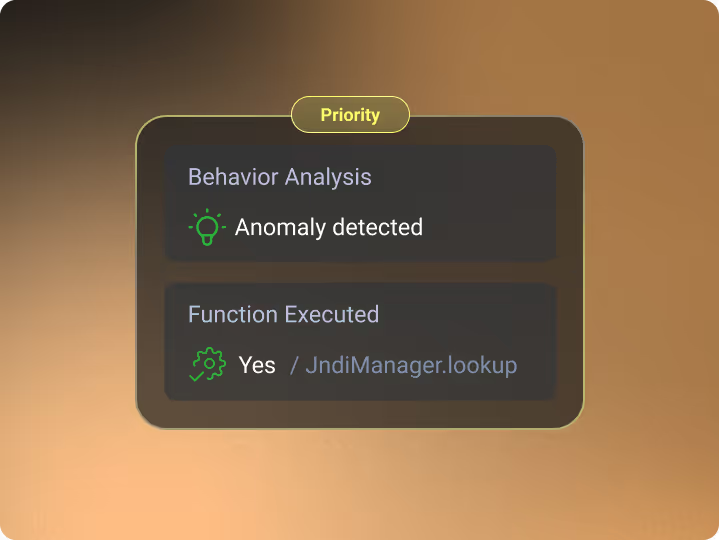
Raven surfaces high-fidelity signals such as:
- Which libraries were invoked
- Which functions executed
- Whether execution matched expected behavior
- Whether execution was blocked or allowed
Faster, More Accurate Investigations
With Raven, Mean Time To Investigate (MTTI) drops dramatically.
During an investigation, Raven answers:
- Did this alert involve real code execution?
- Was the behavior legitimate or abused?
- Was a vulnerable function actually invoked?
Bridge Between SOC and AppSec
With Raven, SOC and AppSec operate from a shared runtime truth.
Raven connects:
- Runtime SCA (what is vulnerable)
- ADR (what is malicious)
- Execution context (what actually happened)
Amplify your SOC with application context
Book a demo
Company News
After an AI-driven campaign hit Korean financial firms, Raven.io enters Korea to stop exploits at runtime, before a CVE exists.
Read more
Security
Classic RASP tools are consolidating under the weight of agents, overhead, and language gaps. See how runtime application security is replacing them.
Read more
Security
A zero-CVE scan proves your dependencies match no published vulnerability. Open source supply chain attacks are built to pass exactly that test.
Read more
